Published 13/06/2024 – est. 4 minutes to read.
The increasing connected car security risk
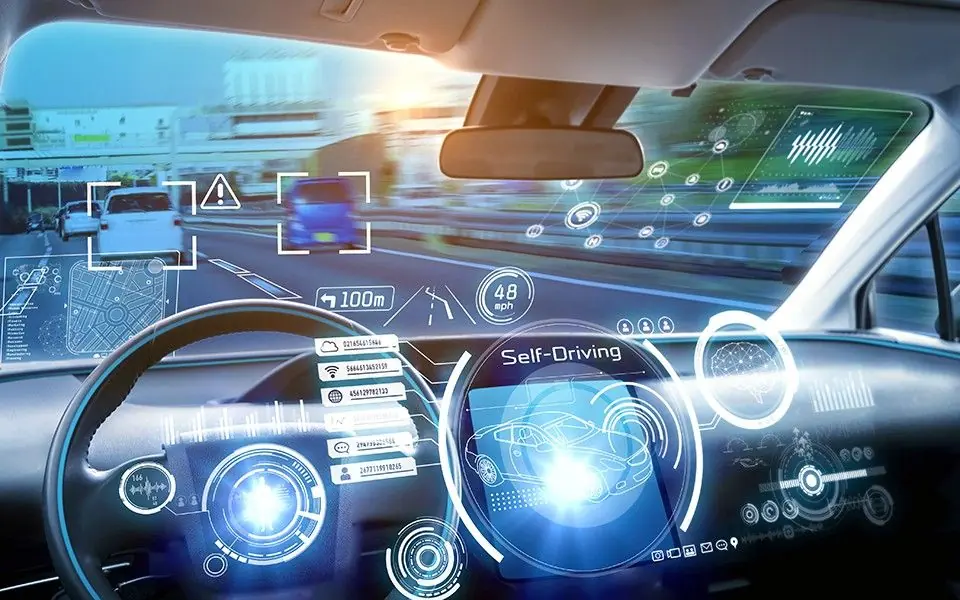
Automotive manufacturers are constantly looking for ways to evolve and improve the driving experience of their vehicles, making them more enjoyable for consumers. Remote functions from apps, improved infotainment systems, and keyless locking or start/stop systems are just a few of the features now included in a vast number of modern vehicles, not just expensive luxury models. It is predicted that all vehicles will be ‘connected’ by 2026.
However, as vehicle technology advances, so does the risk of security breaches by hackers. Despite the improved driving experience, numerous risks to the vehicle’s security now threaten drivers; this article aims to outline these risks and the security measures implemented to prevent such attacks.
What are the risks?
With modern vehicles now having accessibility features such as Bluetooth, Apple Carplay, Android Auto and GPS, risks have heightened in the potential for hackers to gain full control of a vehicle, including heating, music, taking advantage of new RKE (Remote Keyless Entry) systems to gain entry to the vehicle and even the ability to turn off the engine remotely which causes obvious concern for the driver’s safety.
These concerns became reality in 2015, when a Jeep Cherokee was remotely controlled by two hackers, Charlie Miller and Chris Valasek, who took control of the vehicle’s wipers, radio, and, finally, the engine, bringing it to a complete stop. If attacked maliciously, there is significant concern about the potential theft of data (visited locations, etc.), the consumer’s safety while driving, and unauthorised entry into the vehicle using RKE.
What can be done to prevent this?
Software Updates
Both the consumer and the vehicle manufacturer can reduce the risk of an attack occurring by ensuring the vehicle’s software is up to date with the latest patches. Manufacturers have developed an OTA (Over-the-Air) system to address this, enabling the installation of the latest software updates remotely.
OTA software updates are automatically installed when the vehicle is connected to Wi-Fi or a cellular network, or when the vehicle is in use. These OTA updates enhance the vehicle’s infotainment system by improving existing features and adding new ones, updating maps, vehicle firmware, and software, and patching vulnerabilities to strengthen the vehicle’s cybersecurity, ultimately reducing the risk of breaches from malicious threats.
Compliance Frameworks & Certifications for Manufacturers
ISO and SAE have also both come together and issued a joint set of standards, the ISO/SAE 21434 Framework, for automotive cybersecurity engineering, outlining engineering requirements for cybersecurity risk management regarding their concept, product development, production, operation, maintenance and the safe decommission of electrical and electronic (E/E) systems in road vehicles, including components and interfaces.
In addition, UNECE has introduced a mandatory certification of compliance (CSMS) for cybersecurity management systems for all manufacturers of connected vehicles under its new cybersecurity regulations.
Conclusion
The automotive industry has recognised the need for better security, and the introduction of the ISO/SAE 21434 Framework and its associated compliance certification should help improve the security of our connected cars.
Like any technology platform or device, there must be a rigorous vulnerability management program in place so that manufacturers can respond quickly to vulnerabilities or weaknesses in their software that could be exploited by hackers.
When an update is available, if it is not automatically installed, consumers should install it as soon as possible!
Keep up-to-date with our other blogs or to discuss our services, connect directly with our technical team:
Telephone: 0161 706 0244
Email: info@cybersecurityspecialists.co.uk
Related Pages